12-Step Employee Offboarding Security Checklist
A resignation can become a security incident long after the employee’s last day. An active Microsoft 365 account, a saved VPN credential, or an unreturned laptop can give former staff access to confidential files, customer information, and internal systems. This employee offboarding security checklist helps small and midsize businesses close those gaps without disrupting operations.
Offboarding is not an HR task handed to IT at the last minute. It is a coordinated security process involving management, HR, IT, and the employee’s direct supervisor. The goal is straightforward: remove access on time, preserve the business data the company needs, and maintain a clear record of what happened.
Why Employee Departures Create Security Exposure
Most access is granted gradually. Employees receive email accounts, shared folders, cloud applications, finance platforms, remote access tools, mobile device access, administrator permissions, and credentials for vendor portals. Over time, those permissions are easy to lose track of, especially when a company relies on informal processes or several disconnected software tools.
The risk changes depending on the departure. A planned departure with proper notice gives the business time to transfer responsibilities and review access. An involuntary termination, a departing executive, or an employee with financial, legal, healthcare, or administrative privileges requires a tighter process. In those situations, access should be removed during the separation meeting or immediately beforehand, based on advice from HR and legal counsel.
A missed account is not a minor administrative error. It can lead to data loss, fraud, unauthorized file downloads, phishing exposure, or an avoidable compliance problem. A disciplined checklist makes offboarding repeatable, auditable, and faster under pressure.
The 12-Step Employee Offboarding Security Checklist
1. Notify the right people early
HR or management should notify IT as soon as a departure is confirmed. The notice should include the employee’s name, department, manager, final date and time, employment status, and whether the departure requires immediate access removal. IT cannot protect systems on schedule if it learns about the departure after the employee has already left.
Keep the notification limited to the people who need to know. For sensitive exits, designate one decision-maker who can approve timing and confirm each critical action.
2. Build an access inventory
Do not rely only on a list of applications someone remembers using. Review identity systems, password managers, Microsoft 365 or Google Workspace, VPN, remote monitoring tools, line-of-business applications, cloud storage, accounting platforms, CRM systems, VoIP portals, social media accounts, and vendor websites.
The employee’s manager is often essential here. They can identify shared inboxes, client accounts, project folders, or specialized tools that may not appear in a standard IT inventory.
3. Preserve business data before disabling the account
A departing employee may have essential email conversations, files, contacts, calendars, proposals, or customer records stored in their account. Preserve this information according to your data retention policy before deleting anything.
For Microsoft 365 environments, this may involve converting a mailbox to a shared mailbox, assigning an appropriate manager access, forwarding business communications for a defined period, and transferring OneDrive files. Forwarding should be controlled and documented. Indefinite forwarding can create privacy, security, and operational issues.
4. Disable sign-in access at the correct time
Disable the user’s primary identity account, not just their email. This single action should prevent sign-in to connected cloud services where possible. Reset passwords if policy requires it, revoke active sessions and refresh tokens, and invalidate remembered devices.
Timing matters. For a standard resignation, disabling access at the end of the final workday may be appropriate. For a high-risk or immediate departure, access may need to end while the separation meeting is taking place. The approach depends on the role, the circumstances, and company policy.
5. Remove multi-factor authentication methods
Deleting or disabling an account does not always remove registered authenticator apps, phone numbers, hardware keys, recovery email addresses, or backup codes. Remove each registered multi-factor authentication method and confirm that no personal device remains approved for company sign-in.
This step is frequently missed because multi-factor authentication is viewed only as a login protection. It is also an access pathway that must be managed at exit.
6. Revoke remote and privileged access
Disable VPN access, remote desktop permissions, remote support tools, virtual desktop sessions, and access to network management platforms. Then review elevated permissions separately. A former employee should not retain local administrator rights, domain privileges, firewall access, cloud administrator roles, backup console access, or password vault access.
Privileged accounts deserve special attention because they can outlive a normal user account. If the employee knew shared administrative credentials, change them. This includes Wi-Fi administration, network equipment, security systems, vendor portals, and emergency accounts where applicable.
7. Remove access to applications, shared data, and physical systems
Next, remove the user from groups, shared drives, Teams channels, SharePoint sites, CRM roles, accounting systems, payroll platforms, ticketing tools, and document-signing services. Review licenses as well. Removing a license without planning can affect mailbox retention or file ownership, so preserve data first.
Do not overlook physical access. Collect keys, key cards, badges, parking passes, building codes, and access to server rooms, storage areas, or records rooms. If codes were shared widely, changing the code may be safer than assuming it is no longer known.
8. Recover and inspect company equipment
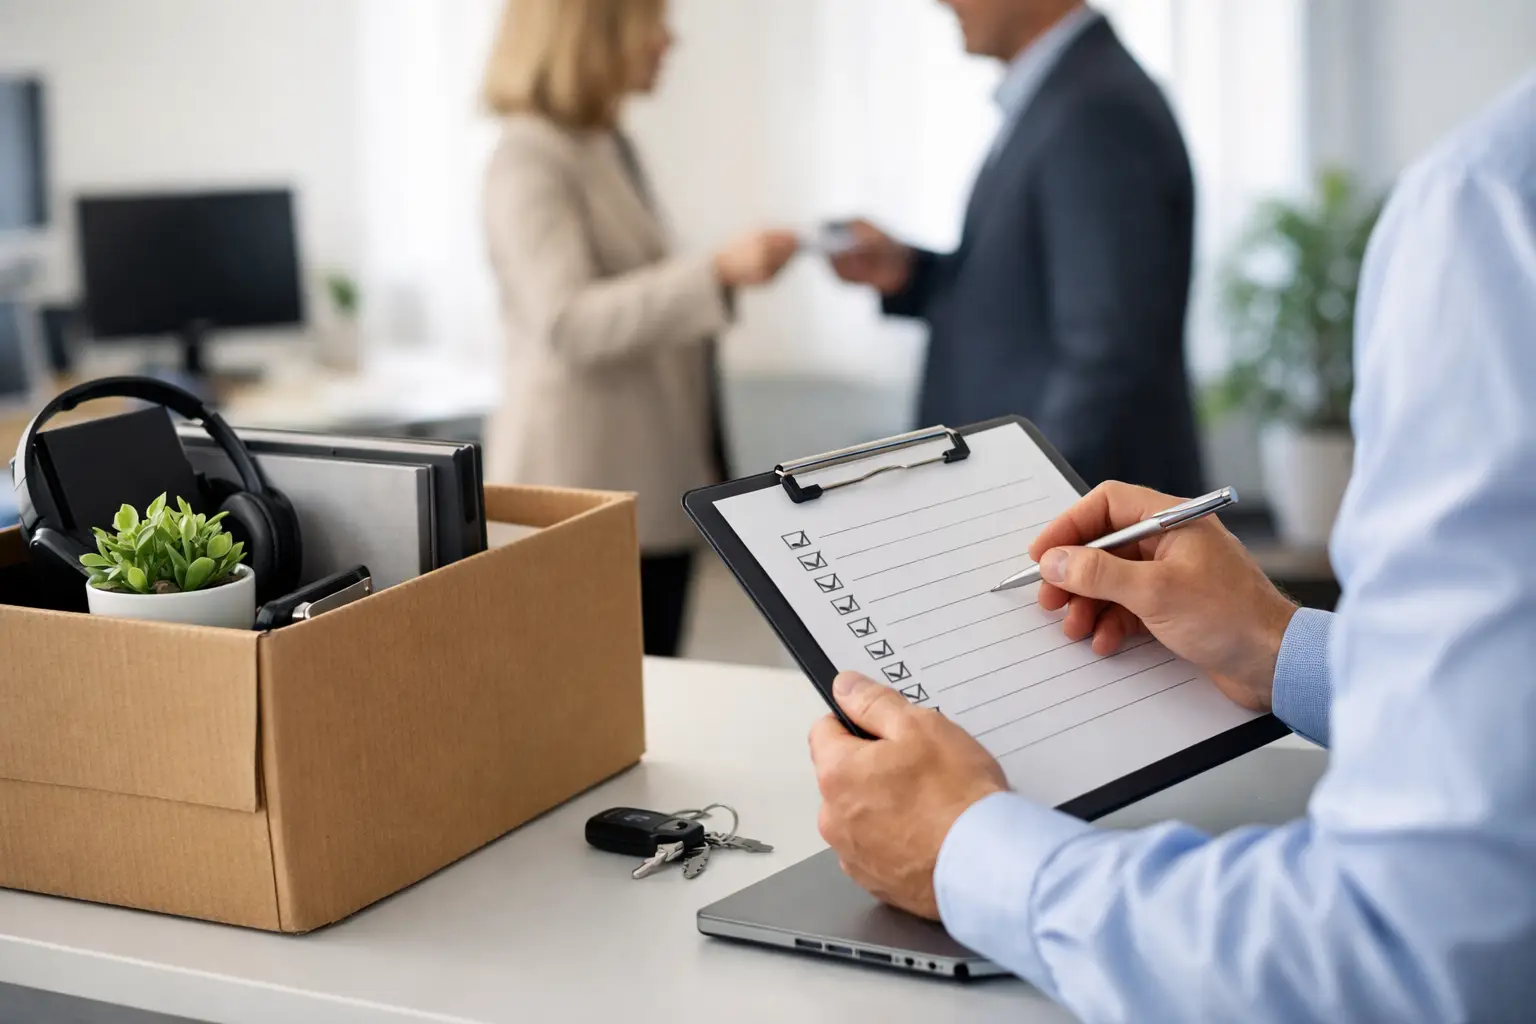
Create a documented asset return process for laptops, monitors, mobile phones, tablets, security tokens, chargers, headsets, and paper records. Match returned equipment to your asset inventory, including serial numbers and assigned users.
Before redeploying a device, IT should confirm that company data is backed up if needed, remove the device from management where appropriate, wipe it using an approved process, apply current updates, and re-enroll it for the next user. A laptop returned in good condition can still contain cached passwords, downloaded files, browser sessions, or locally stored customer data.
9. Transfer ownership and business continuity responsibilities
Security and continuity go together. Reassign ownership of shared mailboxes, recurring meetings, client files, workflows, cloud resources, projects, and vendor relationships. Update emergency contacts and escalation procedures if the departing employee was a primary contact.
This is particularly important for small businesses, where one person may hold key operational knowledge. A secure exit should not leave the finance team unable to process invoices or the operations team unable to reach a critical vendor.
10. Check for unusual activity
Review relevant logs before and after the employee’s final access period. Look for unusual file downloads, large external transfers, forwarding rules, new mailbox delegates, deleted files, unknown devices, or unexpected changes to permissions.
This is not an assumption of wrongdoing. It is a reasonable verification step, especially for employees with access to sensitive information. If activity raises concerns, preserve evidence and involve legal counsel, HR, and security leadership before making conclusions.
11. Document every completed action
Your employee offboarding security checklist should produce a record, not just a verbal confirmation. Document the date and time access was disabled, systems reviewed, assets returned, data transferred, licenses changed, and any exceptions approved by management.
Documentation supports compliance requirements and helps resolve disputes later. It also improves the next offboarding event by revealing systems that were missed, duplicate accounts that exist, or ownership gaps that need to be fixed.
12. Review the process after the departure
Once the immediate work is complete, take a short look at what created friction. Did HR notify IT late? Did the company lack an accurate software inventory? Was a critical password shared rather than stored in a controlled vault? Were company files saved on a personal device?
These are operational weaknesses worth correcting before the next employee leaves. A mature process becomes easier over time because access, assets, ownership, and documentation are maintained throughout employment, not reconstructed during an exit.
Make Offboarding a Managed Security Workflow
A checklist is only effective when it has owners, deadlines, and verification. HR should own the personnel event and timing. IT should own access removal, data protection, device handling, and documentation. Managers should own responsibility transfer and confirm that business access has been reassigned correctly.
For many businesses, the practical challenge is visibility. There may be no centralized record of software subscriptions, administrator accounts, devices, or employee permissions. That creates a dangerous dependence on memory at exactly the moment a fast, accurate response is needed.
Krove helps businesses turn offboarding into a controlled workflow through managed user access, Microsoft 365 administration, endpoint management, security monitoring, and documented IT processes. The objective is not simply to close an account. It is to protect the company without leaving teams unable to do their jobs.
The best time to test your offboarding process is before a difficult departure forces the issue. Assign the owners, verify the access inventory, and run the checklist against a recent role change or test account. A few hours of preparation can prevent a former employee’s forgotten access from becoming your next business interruption.